AI & PRIVACY  | The Seattle Times
By Jayati Ramakrishnan |
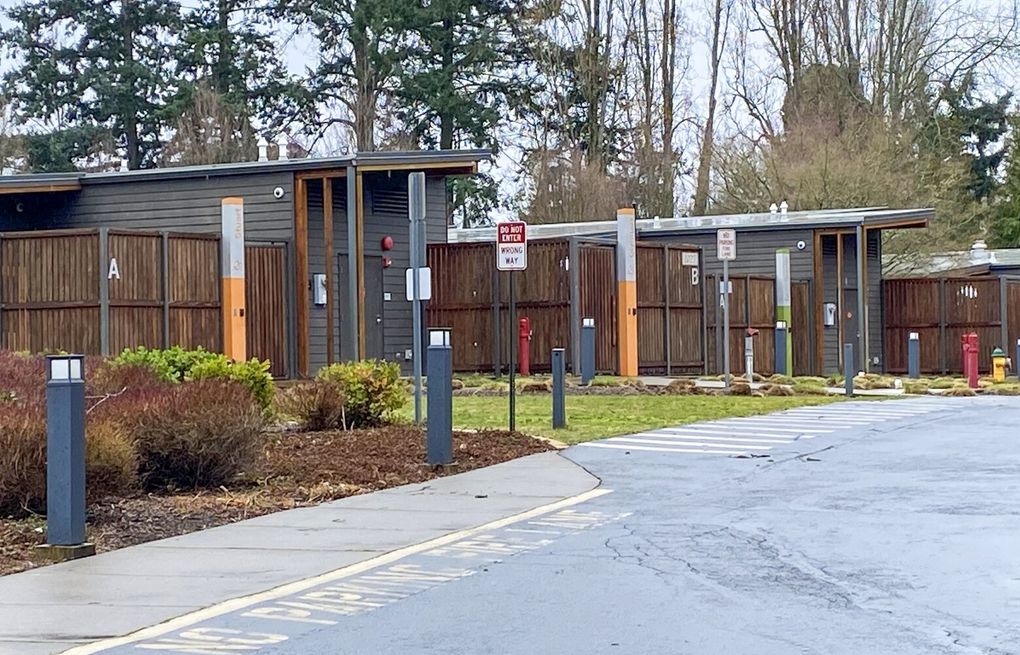 Image: The Seattle Times (seattletimes.com). What happened: Washington's social services department says patient names, diagnoses and medications may have been exposed at two state-run mental-health facilities after staff used AI without approval to draft notes, affecting 12 youth at Lake Burien and 4 at Western State Hospital. Key points: - A coworker reported the Lake Burien employee in July for drafting case-note summaries with a personal ChatGPT account, and the state later found other patients were involved too.
- The state says Social Security numbers weren't exposed and it found no sign of further disclosure, but admits it doesn't know how ChatGPT stores the data.
- Agency policy bars unapproved AI use; the employee was instructed on IT security and confidentiality, then told to delete all prompts before closing the account, which they did.
- University of Washington AI researcher Bill Howe suggests locally controlled models or strong vendor contracts, but warns HIPAA compliance gets harder as AI memory systems grow more complex.
| Why this matters: Pasting client details into a consumer chatbot to speed up documentation feels like a harmless shortcut, but this case shows how quickly it can become a potential privacy breach affecting vulnerable clients. Whether or not you use AI, it's a good moment to make sure everyone in your practice knows which tools are approved and HIPAA-aligned. |
Read original story | 
Leave a Reply